CDD Filings Digital Consumer
Program Areas
-
Press Release
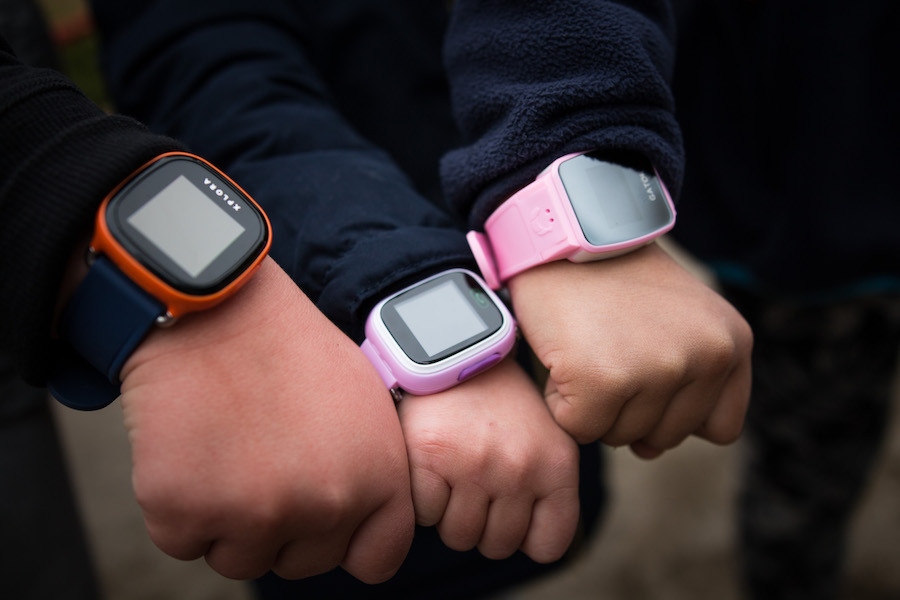
“Smartwatches” For Parents to Monitor Young Children Actually Pose a Danger to Kids’ Welfare—Report
Groups call for investigation and action by U.S. and EU Regulators, including FTC
WASHINGTON, DC – October 18, 2017—A number of brands of “smartwatches” intended to help parents monitor and protect young children have major security and privacy flaws which could endanger the children wearing them. A coalition of leading U.S. child advocacy, consumer, and privacy groups sent a letter to the Federal Trade Commission (FTC) today, asking the agency to investigate the threat these watches pose to children. Smartwatches for children essentially work as a wearable smartphone. Parents can communicate with their child through the mobile phone function and track the child’s location via an app. Some product listings recommend them for children as young as three years old. Groups sending the letter to the FTC are the Electronic Privacy Information Center (EPIC), the Center for Digital Democracy (CDD), the Campaign for a Commercial-Free Childhood (CCFC), the Consumer Federation of America, Consumers Union, Public Citizen, and U.S. PIRG. The advocacy groups are working with the Norwegian Consumer Council (NCC), which conducted research (link is external) showing that watches sold in the U.S. under the brands Caref and SeTracker have significant security flaws, unreliable safety features, and policies which lack consumer privacy protections. In the EU, groups are filing complaints in Belgium, Denmark, the Netherlands, Sweden, Germany, the UK, and with other European regulators. “By preying upon parents’ desire to keep children safe and, these smart watches are actually putting kids in danger,” said CCFC’s Executive Director Josh Golin. “Once again, we see Internet of Things products for kids being rushed to market with no regard for how they will protect children’s sensitive information. Parents should avoid these watches and all internetconnected devices designed for kids.” The NCC’s research showed that with two of the watches, a stranger can take control of the watch with a few simple steps, allowing them to eavesdrop on conversations the child is having with others, track and communicate with the child, and access stored data about the child’s location. The data is transmitted and stored without encryption. The watches are also unreliable: a geo-fencing feature meant to notify parents when a child leaves a specified area, as well as an “SOS” function alerting parents when a child is in distress, simply do not work. The manufacturers’ data practices also put children at risk. Some devices have no privacy policies at all, and the policies that do exist lack basic consumer protections, including seeking consent for data collection, notifying users of changes in terms, and allowing users to delete stored data. "The Trump Administration and the Congress must bring America’s consumer product safety rules into the 21st century,” said Jeff Chester of the Center for Digital Democracy. “In the rush to make money off of kids’ connected digital devices, manufacturers and retailers are failing to ensure these products are truly safe. In today’s connected world that means protecting the privacy and security of the consumer—especially of children. Both the FTC and the Consumer Product Safety Commission must be given the power to regulate the rapidly growing Internet of Things marketplace.” The Caref (branded Gator in Europe) and SeTracker smartwatches are available online through Amazon. The groups have asked the FTC to act quickly to investigate these products, and they advise parents to refrain from buying the products because of the danger they could pose to children. The NCC, which conducted the testing of the watches, advises consumers who have already purchased the watches to stop using them and uninstall the app. “The Federal Trade Commission must be proactive in protecting consumers—especially vulnerable young children—from harmful products that abuse technology for the sake of profit,” said Kristen Strader, Campaign Coordinator for Public Citizen. “Smartwatches and similar devices must be absolutely safe and secure before they are released to the public for sale.” Ed Mierzwinski, Consumer Program Director at U.S. PIRG, said, "Companies making any internet-connected devices, but especially for children, need to ensure that privacy and security are more than breakable — or worse, hackable — promises." Katie McInnis, technology policy counsel for Consumers Union, said, “When a company sells a smartwatch aimed at children, it must ensure the product is safe and secure. The FTC should launch an investigation into the privacy and security concerns surrounding these products to make sure families are safe.” The same trans-Atlantic coalition persuaded government authorities and retailers last December (link is external) that the internet-connected dolls Cayla and i-Que Robot were spying on children and threatening their welfare, and retailers removed the toys from store shelves. The FBI subsequently issued a warning to consumers (link is external) that internet-connected toys could put the privacy and safety of children at risk. --- For more information, please see the following: Letter to FTC by coalition of leading U.S. child advocacy, consumer, and privacy groups (link below) Press Release by US coalition of leading U.S. child advocacy, consumer and privacy groups (link below) #WatchOut Report by Norwegian Consumer Council (link below) Press Release by Norwegian Consumer Council (link below) #WatchOut English - YouTube (http://bit.ly/2ghNoD1 (link is external)) #WatchOut - longer video explainer on security flaws 4:30 mins - YouTube (http://bit.ly/2xLYSVv (link is external)) -
January 27, 2017 - The Center for Digital Democracy and 18 media justice, consumer protection, civil liberties, and privacy groups strongly urge congressional leaders to oppose the use of the Congressional Review Act (CRA) to adopt a Resolution of Disapproval overturning the FCC’s broadband privacy rules.---Click the link below for the full PDF of the letter.
-
Re: Exploring Special Purpose National Bank Charters for Fintech Companies Dear Comptroller Curry: The Center for Digital Democracy and U.S. Public Interest Research Group (U.S. PIRG) agree with the consumer, civil rights, and community groups and their separately filed group letter in which they expressed strong opposition to the proposed new federal nonbank lending charters. U.S. PIRG also signed and concurs with the detailed comment from National Consumer Law Center et al. The Office of the Comptroller of the Currency (OCC) must not undermine state rate caps; must not weaken states’ ability to oversee lenders and act to prevent harmful lending practices; and the OCC must not undermine efforts to provide fair and inclusive lending practices, particularly for people of color and low- and moderate-income consumers, in the areas where they operate. Further, the OCC must not allow nonbank lenders to engage in practices that violate privacy rights, or engage in unfair data and marketing practices. State laws often operate as the primary line of defense for consumers and small businesses. The OCC’s charter proposal inadequately protects consumers from these harmful practices and it should not take state law enforcers off the beat of preventing these practices. Center for Digital Democracy and U.S. PIRG file this supplemental comment to focus on the digital rights and consumer privacy concerns raised by the use of opaque Big Data algorithms used by Fintech firms. These practices increasingly threaten consumer privacy and the OCC must also take them into account when considering non-bank special purpose charters. An ongoing and increasingly challenging issue confronting citizens and consumers is the new threats to their privacy and their ability to control how personal and non- personal data about their online and offline behavior are collected and used by online financial services companies. The use of personal data by Fintech companies is pervasive and touches every aspect of their business operation, including marketing, customer loyalty management, pricing, fraud prevention, and underwriting. Fintech companies use many new on- and offline data sources, either directly collecting data from consumers or relying on third parties for Big Data analytics to classify consumers and to make predictions about them. Assigning individuals to socially constructed classifications and then making inferences about them based on group profiles is likely to have consequences that are not well understood and may further increase social inequities. Consumers’ privacy is increasingly undermined and no adequate protections are in place. The OCC must not allow an expansion of these practices via a federal charter that does not provide for adequate privacy safeguards. The OCC must proactively investigate unfair marketing practices and not grant national licenses without affirmative protections. Fintech companies are using Facebook, Instagram, and other digital behavioral data that combine data and interactive experiences to influence consumers and their social networks. Sophisticated data-processing capabilities allow for more precise micro-targeting, the creation of comprehensive profiles, and the ability to act instantly on the insights gained from consumer behaviors. Targeted and highly personalized marketing offers can be intrusive and foster consumer behaviors that are not in the best interest of the individual. Behavioral science shows that consumers are susceptible to ‘nudges’ which raises concerns about the risk of financial institutions taking advantage of the behavioral biases and limitations of consumers. Increasing personalization which Big Data makes possible, could also reduce the comparability of products, making it harder for consumers to compare one offer with another which could have an impact on market competition. Similarly, lack of transparency around the processing of data and automated algorithms may lead to increasing information asymmetries between the financial institution and the individual and thus consumers are left with less awareness and a lack of understanding and control over important financial decisions. These practices happen behind the scenes and can only be addressed by a vigilant regulator. The OCC should not allow fintech companies to operate a national license without properly addressing these data practices. The OCC must also not allow nonbank lenders or partner depository institutions to engage in unfair and discriminatory lending practices. The use of ‘alternative data’ sources can be the cause of bias or contain errors and may lead to consumer harm or unfairness. While alternative credit scoring can be a boon for the underbanked, there need to be standards and safeguards to ensure that any new data are not biased and that their use may not lead to unintended consequences. While industry has argued that increased automation will help expand access to credit and lower costs overall, credit models that are more “accurate” may lead to a more stratified society, as it will leave those at the bottom potentially excluded from credit forever. Models that judge individuals against group profiles based on past data inevitably incorporate elements of past inequality and discrimination. Communities of color are thus most vulnerable. Unless additional policies are put in place to address these consequences, inequality is likely to become more entrenched the more we rely on models for risk evaluations. Fintech platforms must comply fully with the requirements of the Fair Credit Reporting Act and Equal Credit Opportunity Act. In conclusion, the OCC must not grant new federal nonbank lending charters that would give firms free rein to use unfair data and marketing practices. Instead the OCC must proactively mitigate risks from unfair data, marketing, and lending practices that threaten to undermine privacy, consumer rights and economic inclusion. Sincerely, Jeff Chester and Katharina Kopp Center for Digital Democracy Edmund Mierzwinski U.S. PIRG Recommended further reading: BIG DATA MEANS BIG OPPORTUNITIES AND BIG CHALLENGES: Promoting Financial Inclusion and Consumer Protection in the “Big Data” Financial Era U.S. PIRG Education Fund and Center for Digital Democracy, 27 March 2014 Available at http://www.uspirg.org/reports/usf/big-data-means-big-opportunities-and-b... (link is external)
-
Center for Digital Democracy, Center for Democracy & Technology, Consumer Action, Consumer Federation of America, Consumer Federation of California, Consumers Union, Electronic Privacy Information Center, National Association of Consumer Advocates, National Consumers League, Benton Foundation, Common Sense Kids Action, and Privacy Rights Clearinghouse file this brief to highlight the potential far-reaching ramifications of this case as well as the degree to which the panel decision breaks from century-long precedent, thereby creating a sharp split among the courts of appeals.First, the panel opinion raises issues of exceptional importance. If allowed to stand, the ruling could immunize from FTC oversight a vast swath of companies that engage to some degree in a common carrier activity. This result is unprecedented, deeply disruptive to the market, and at odds with Congress’s intent. Many of the world’s largest companies offer broadband Internet or other common carriage service. These highly diverse companies could harm consumers by committing acts that are deceptive or unfair, breach privacy commitments, fail to provide reasonable security for sensitive personal data, violate any of the seventy consumer protection statutes Congress has directed the FTC to enforce, or, as in the AT&T case, deliberately omit critical information about the services a company provides – and nonetheless escape FTC enforcement. No other federal agency has authority to fill this void.Second, the panel’s decision creates a deep Circuit split by breaking from the 100-year-long understanding that the term “common carrier” is defined by activities, not status. Departing from established norms of statutory construction, the panel failed to heed settled interpretive rules requiring that exemptions from antitrust laws be construed narrowly; that remedial statutes be read broadly to effectuate their purposes; and that an agency’s interpretation of its organic statute be accorded deference. The panel’s inversion of decades of precedent creates a substantial regulatory gap and puts the Ninth Circuit directly in conflict with the D.C. and Second Circuits.---For the full argument, see the attached PDF.
-
Cross-Device Privacy Must be Protected by FCC Proposed Rule on Broadband ISPs
Geolocation & Cross Platform and Application Data is Sensitive information. AT&T expands cross-device targeting
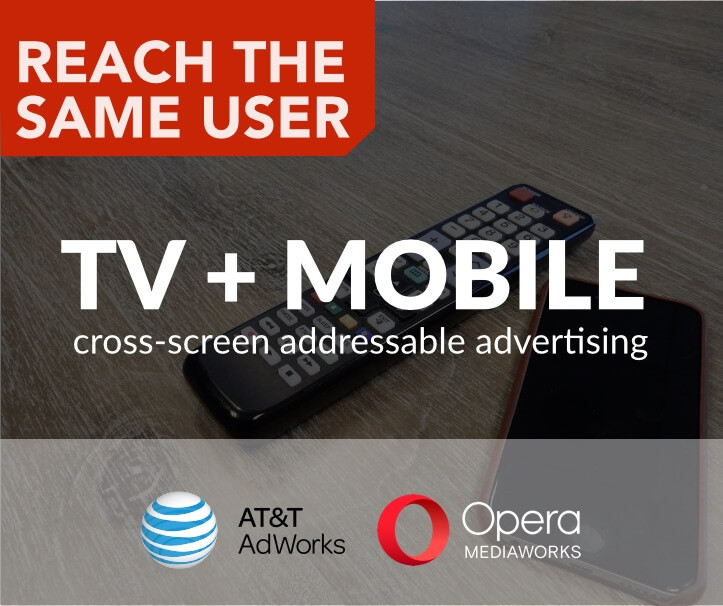
... ISPs are engaged in cross-device tracking of its subscribers and customers which allow them to target advertising at the individual and household level. Exemplary for all ISPs, we are highlighting AT&T’s efforts in this area. AT&T is expanding its cross-device tracking in order to target individuals on their mobile device after collecting and analyzing their data using the company's internal data and analytics capabilities. In a recent interview, AT&T AdWorks President Rick Welday explained that by the end of this year AT&T will allow marketers to “advertise in 14 million addressable households, 30 million mobile devices and millions of streams within the DirecTV app.” While AT&T may claim that its cross-device tracking is done “anonymously,” that is merely a euphemism to obscure the invasion of privacy that underlies such practices. Mr. Welday explains that AT&T’s data-driven monitoring of its customers enables it to develop dossiers that reveal whether their users are a new homeowner, a new parent, or in the market for an automobile. In its trials with cross-device targeting, AT&T worked with leading Fortune 100 brands as well as promoting its own “AT&T Mobility Wireless” service. The Fortune 100 companies that AT&T worked with likely provided their own so-called first-party data to be used for such cross-device targeting. This illustrates the operational realities today for consumer profiling data, where data are no longer shared with advertisers, but rather advertisers provide such data to ad-delivery platforms (such as AT&T's) for increasingly granular targeting.[3] Linking devices (and the application history on and geolocation on of those devices) to a particular consumer via a unique identifier should be prohibited, unless the ISP has obtained affirmative, express consent (opt-in). The rule’s definition of ‘sensitive information’ must therefore reflect industry practices and include any data elements that allow for this kind of cross-device tracking. The final rule must give ISP customers control over their data, and before companies can proceed with targeted advertising, they must obtain an opt-in consent from their customers. We are particularly concerned that without such safeguards the rules would allow for a by-passing of requirements of the Children’s Online Privacy Protection Act, by using insights gained via cross device tracking to target children without parental consent. Finally, we urge the Commission to affirm in its final rule the need for safeguards against any unauthorized attempts to re-link devices (and its app usage history and geolocation information) to associate them with one user. CDD respectfully urges the FCC to enact its proposed safeguards as soon as possible to help address the further eroding of Americans’ privacy by ISPs. -
Electronic Privacy Information Center & CDD Defend Privacy Rights of WhatsApp Users
WhatsApp plan to transfer user data to Facebook is unlawful, groups tell Federal Trade Commission (FTC)
Washington, DC (August 29, 2016) – The Electronic Privacy Information Center (EPIC) and the Center for Digital Democracy (CDD) today filed a complaint with the Federal Trade Commission, stating that the WhatsApp plan to transfer user data to Facebook is unlawful and that the FTC is obligated to block the proposed change in business practices.The EPIC-CDD complaint responds to a recent announcement from WhatsApp that the company plans to disclose the verified telephone numbers of WhatsApp users to Facebook for user profiling and targeted advertising.“When Facebook acquired WhatsApp, WhatsApp made a commitment to its users, to the Federal Trade Commission, and to privacy authorities around the world not to disclose user data to Facebook. Now they have broken that commitment,” said Marc Rotenberg, President of EPIC. “Clearly, the Federal Trade Commission must act. The edifice of Internet privacy is built on the FTC’s authority to go after companies that break their privacy promises.” Facebook and WhatsApp are the two largest social network services in the world. According to Wikipedia, WhatsApp has over one billion users. Facebook purchased the company in February 2014 for 19.3 billion dollars.EPIC Consumer Protection Counsel Claire Gartland explained, “In 2014, the FTC said that WhatsApp had to obtain affirmative consent to transfer user data to Facebook. There was an opt-out provision but that only applied to new information. Since WhatsApp intends to transfer user telephone numbers, which is not new data, it must obtain opt-in consent.”Gartland continued, “The phone number may also be the single most valuable piece of personal data obtained by WhatsApp. WhatsApp users are required to provide a verified phone number to use the service. And the phone number provides a link to a vast amount of personal information.”“The proposed change – an opt-out for data previously obtained – is exactly what the FTC said WhatsApp could not do,” said Gartland. “The transfer is only allowed if the consent is opt-in.”“The FTC has an obligation to protect WhatsApp users. Their personal information should not be incorporated into Facebook’s sophisticated data driven marketing business,” said Katharina Kopp, Ph.D., and CDD’s Director of Policy. “Data that was collected under clear rules should not be used in violation of the privacy promises that WhatsApp made. That is a significant change that requires an opt-in, according to the terms the FTC set out. It’s not complicated. If WhatsApp wants to transfer user data to Facebook, it has to obtain the user’s affirmative consent.”In 2011, EPIC, CDD and more than a dozen consumer privacy organizations pursued a successful complaint at the FTC that led to a twenty-year consent order after Facebook changed user privacy settings in a way that made users' personal information, such as Friend lists and application usage data, more widely available to the public and to Facebook’s business partners.Former FTC Chair John Liebowitz said at the time, “Facebook is obligated to keep the promises about privacy that it makes to its hundreds of millions of users. Facebook's innovation does not have to come at the expense of consumer privacy. The FTC action will ensure it will not."When Facebook proposed to acquire WhatsApp in 2014, EPIC and CDD said the FTC must protect the privacy of WhatsApp users. The FTC said that WhatsApp must continue to honor its privacy promises to consumers.The FTC warned, “If the acquisition is completed and WhatsApp fails to honor these promises, both companies could be in violation of Section 5 of the Federal Trade Commission (FTC) Act and, potentially, the FTC's order against Facebook.”The Federal Trade Commission has previously undertaken investigations against many firms that have engaged in unfair or deceptive trade practices.The Electronic Privacy Information Center (EPIC) (link is external) is a public interest research center in Washington, DC. EPIC was established in 1994 to focus public attention on emerging privacy and civil liberties issues and to protect privacy, freedom of expression, and democratic values in the information age. EPIC maintains one of the most popular privacy web sites in the world - epic.org (link is external) - and pursues a wide range of program activities including policy research, public education, litigation, publications, and advocacy. The Center for Digital Democracy (CDD) is recognized as one of the leading consumer protection and privacy organizations in the United States. Since its founding in 2001 (and prior to that through its predecessor organization, the Center for Media Education), CDD has been at the forefront of research, public education, and advocacy protecting consumers in the digital age.REFERENCESEPIC/CDD, In the Matter of WhatsApp: Complaint, Request for Investigation, Injunction, and Other Relief (Aug. 29, 2016),https://epic.org/privacy/ftc/whatsapp/EPIC-CDD-FTC-WhatsApp-Complaint-20... (link is external)FTC, “Enforcing Privacy Promises” (2016),https://www.ftc.gov/news-events/media-resources/protecting-consumer-priv... (link is external)FTC Press Release, “FTC Notifies Facebook, WhatsApp of Privacy Obligations in Light of Proposed Acquisition” (Apr. 10, 2014),https://www.ftc.gov/news-events/press-releases/2014/04/ftc-notifies-face... (link is external)FTC Letter to FB and WhatsApp, "Letter From Jessica L. Rich, Director of the Federal Trade Commission Bureau of Consumer Protection, to Erin Egan, Chief Privacy Officer, Facebook, and to Anne Hoge, General Counsel, WhatsApp Inc.” (Apr. 10, 2014),https://www.ftc.gov/news-events/press-releases/2014/04/ftc-notifies-face... (link is external)FTC, "Facebook Settles FTC Charges That It Deceived Consumers By Failing To Keep Privacy Promises” (2011),https://www.ftc.gov/news-events/press-releases/2011/11/facebook-settles-... (link is external)FTC Consent Order with FB (2011),https://www.ftc.gov/news-events/press-releases/2012/08/ftc-approves-fina... (link is external)EPIC, In re WhatsApp,https://epic.org/privacy/internet/ftc/whatsapp/ (link is external)EPIC, In re Facebook,https://epic.org/privacy/inrefacebook/ (link is external)### -
In Reply Comments to FCC, CDD Explains Why Consumers Require Privacy Protection from Broadband Network Providers
Filing counters industry claims, including on consumer choice and role of digital ad market. Provided new evidence on growth of ISP "Big Data" commercial consumer profiling practices. CDD and colleagues also file on failure of multistakeholder process and also need to protect privacy of children and adolescents
We believe that the absence of any FCC rulemaking to protect the privacy of broadband customers would significantly add to the already prevalent sense of confusion and sense of loss of control among broadband internet customers under the existing FTC regime. Instead, the proposed rules will give ISP customers much needed control over their data and are much more likely to increase consumer confidence. Second, we would like to emphasize that current BIAS provider data practices already undermine the privacy of their customers and that they are in the process of further building out their powerful data management capabilities. Due to these practices and their significant position in the data eco system, BIAS providers are a growing and significant marketplace force in digital advertising. Contrary to companies’ and trade associations’ claims, we see no evidence that giving BIAS providers’ customers effective privacy choices will limit the online advertising industry to flourish. The American public wants to see its privacy protected and needs the safeguards proposed by the Commission. Nothing less will limit the expansion of an unprecedented intrusion of BIAS providers into the most private aspects of American consumers’ lives. The Commissions’ proposed rules are needed to protect individual autonomy and the fundamental right to privacy and self-determination. see attached for the complete Reply Comment Also attached is joint filing showing how the so-called "Multistakeholder" Process on privacy, organized by the Department of Commerce, has repreatedly failed to protect the public. -
In the Matter of Petition of Public Knowledge, Center for Digital Democracy, Consumer Watchdog, Consumer Federation of America, and TURN —The Utility Reform Network Introduction: 47 U.S.C. §551 and 47 U.S.C. § 338(i) (collectively referred to as “privacy rules”) require that cable and satellite providers (herein referred to as “cable operators”) obtain the “written or electronic consent of the subscriber concerned” prior to the collection and use of that information for advertising purposes. Cable operators are also required to provide a written statement to their subscribers, which clearly and conspicuously informs the subscriber of the nature of the use of their personally identifiable information. Through these rules, Congress and the Federal Communications Commission have emphasized the importance of giving consumer’s control over how their information is being used. Despite this, cable operators have continued to use large amounts of their customers’ data without properly obtaining customer consent or informing subscribers of the extent of the use of their information. The Commission should enforce the relevant privacy provisions to ensure that cable operators only use subscriber information when they have the consent required by law. Cable Operators Collect and Share Large Amounts of Customer Data to Generate Targeted Advertising. The use of consumer data to target consumers for advertising is on the rise. Exactly how and to what extent cable operators are leveraging their customer’s data has been extensively documented in a recent report by the Center for Digital Democracy. Cable operators increasingly gather their customers’ personal information, share and combine that information with third parties, and use it to target customers for advertising on an individual level. Verizon, Comcast, Google, AT&T, Time Warner, Cablevision and others have incorporated powerful layers of data collection and digital marketing technologies to better target individuals. AT&T’s TV Blueprint, for example, “gives advertisers working with AT&T the ability to reach people based on factors like device, operating system, whether or not they’re heavy data users or the status of their carrier contract,” using “sophisticated second-by-second set- top box data” and other information. AT&T pulls data “from millions of set-top boxes” and analyzes consumer viewing history and uses these data to target consumers based on their viewing profile. Companies like Cablevision leverage granular data and precise details of household viewing behavior, and combine it with third-party data covering other intimate details of consumers’ lives to analyze and target specific individuals with video advertising across a range of screens. In their own words, “this set-top box level targeting lets marketers target customers that fit particular trends, profiles, demographics and attributes, and they can also pair the Cablevision data with their own or third-party data.” Cablevision and AT&T are not alone in their pervasive use of consumer data. Comcast recently acquired Visible World, which boasts of using data “from millions of enabled Smart TVs” as part of its advertising targeting service. Data points used to target consumers include income, ethnicity, education level, what kind of car they drive, purchase history, and location of their residence. Further, Comcast has acquired companies like This Technology, which is capable of inserting personalized content into network streams—including advertising messages tailored for specific individuals. These programs illustrate how cable providers give advertisers the ability to easily access and use a customer’s information, without that customer knowing the extent to which that information is being used. While these practices are broadly indicative of the ways many cable operators improperly use subscriber data, AT&T, Cablevision, and Comcast are among the most egregious. The Commission should investigate these practices and find that they violate the privacy rules. --- Full filed complaint attached below.
-
CDD Calls on FCC to Protect Consumer Privacy on Broadband Networks
Comments show ISP "Big Data" techniques used to target consumers and discusses limited capabilities of FTC
The Center for Digital Democracy (CDD), a nonprofit organization representing the interests of consumers in the digital marketplace, strongly supports the Federal Communication Commission’s (FCC) proposal to empower individuals to make effective decisions regarding their privacy on broadband networks. Broadband Internet access service (BIAS) plays a powerful and distinctive role in the commercial digital media marketplace, requiring precisely the set of sensible safeguards offered by the Notice of Proposed Rulemaking (NPRM). CDD believes it is entirely necessary and consistent with the Communications Act that the commission extend longstanding consumer-protection policies for the telephone network into the modern broadband context. The role of the network in the broadband marketplace has a distinct purpose compared to so-called “edge” content providers: to facilitate a fairly managed and efficient connection between the subscriber/consumer and the content and/or services of their choice. Given their network-management role, BIAS providers have unique capabilities in terms of monitoring the communications and activities of their subscribers, enabling the capture and use of an extensive array of personal and other consumer information. Positioned by necessity at the center of subscribers’ wireline or wireless broadband use, and holding a “digital key” that can help analyze much of their users’ digitally connected behaviors, BIAS providers have unlimited opportunities to influence the decisions consumers make via data-collection-related applications and services. Consumers today confront a far-reaching and largely invisible data-gathering apparatus that tracks and analyzes their every move online. For example, as the FTC has acknowledged, the growth of cross-device tracking, enabling the identification of a particular consumer’s use of personal computers, mobile phones, tablets, and increasingly even television, and combining multiple sources of data for the development of a targeting profile, illustrates how recent advances in digital data collection pose growing threats to consumer privacy. Indeed, the journal of the Association of National Advertisers explained just last month, “cross-device marketing … allows unprecedented access to individual consumers via personal or shared household devices. … Data-driven cross-device marketers gain exclusive access to a slew of advantageous marketing enhancements, including consistent messaging across all devices … .” Leading BIAS providers promise such cross-device targeting capabilities. Lacking the ability to enact regulations to protect privacy (except for children 12 and under), the FTC has been powerless to ensure consumer protection from cross-device tracking practices, let alone from the growing myriad of practices that gather consumer data from social media, mobile app, online video usage, programmatic targeting, and many other practices. Without the authority to issue regulations on privacy-related matters connected to consumer financial services, for example, the FTC has been forced to rely on its Section 5 authority related to unfair and deceptive practices. In practical terms, this has enabled the digital-data industry to recognize that there are no real constraints to their rapidly expanding collection, analysis, and use of consumer data. The FTC has long recognized that its inability to issue regulations has placed the agency at a serious disadvantage, and has called for the enactment of new regulatory authority. For example, as former FTC Chairman Jon Leibowitz testified before Congress in 2009, in order for the agency “to perform a greater and more effective role protecting consumers … changes in the law and additional authority to promulgate needed rules …” are required. As CDD explained in its March 2016 report on the growth of digital data gathering by leading ISPs (and filed separately in this proceeding), companies such as ATT, Comcast, Verizon, Cablevision, and Charter have made significant investments in their ability to capture, process, and take advantage of a consumer’s information across all the devices they use daily. They are using cloud- and IP-based management systems to deliver data-connected advertising and marketing; have invested in or allied with real-time programmatic marketing technologies that, in milliseconds, make personalized ad-related decisions on which consumers to target and for what product; and have acquired numerous companies that strengthen their hold and use of consumer information, including data gathered by their consumers’ use of apps, online video, and mobile phones... Key characteristics of the BIAS data collection apparatus include: [see attached comments for full submission] -
Set-top Box market should be open, but consumers and privacy protected, CDD tells FCC
Calls for Safeguards for sensitive data, including protecting youth, seniors, and use of ethnic/racial information in FCC"s Navigational Device Proceeding
The Center for Digital Democracy (CDD), which works to empower and protect consumers in the digital marketplace, endorses the Federal Communications Commission’s (FCC) important proposal to provide both choice and competition in the provision of navigational devices for video and related content. CDD strongly believes that the FCC should proceed with its plan to allow third parties to build and sell navigational devices. We support giving these developers/providers access to the information proposed in the NPRM, including Service Discovery, Entitlement, and Content Delivery data. For decades, a handful of powerful cable—and now also telephone—companies have held a monopoly over the design, availability, and use of set-top boxes. This has resulted in greater costs to subscribers, including an especially unfair burden on low- or limited-income consumers. The set-top stranglehold has impaired competition and programming diversity, and has undermined consumer privacy. --- Full PDF of filing attached.